


I ran into a school. Let's make up for something
References:
(reference to previous article)
Decryption tool: (and algorithm brief, copyed)
♪ a stolen picture ♪
Some of the details aren't so close to where they might be wrong
Tea(tiny encryption algorithm)
It was invented by david j. Wheeler of cambridge university, england, 1994
Group encryption algorithms are very simple to achieve and usually require only a few lines of code。
The tea algorithm uses 64-bit specified grouping and 128-bit key, using the feistel grouping encryption framework, which requires 64-wheeling, but the tea author believes that 32 rounds are sufficient, so the 32-wheeling encryption leads to 64-digit encryption。
The algorithm uses a mystical constant as a multiple, which is derived from the gold ratio to ensure that each round of encryption is different。
Recommended & default: δ = "(√5 - 1) 231" = 0 x 9e3779b9
8 bytes per group (64 bit)
Secret
Same thing
Key
16 bytes (128 bit)
Rounds
32 (recommended) ~ 64
Encryption
Rounds: 32 rounds
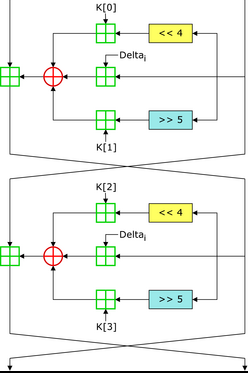
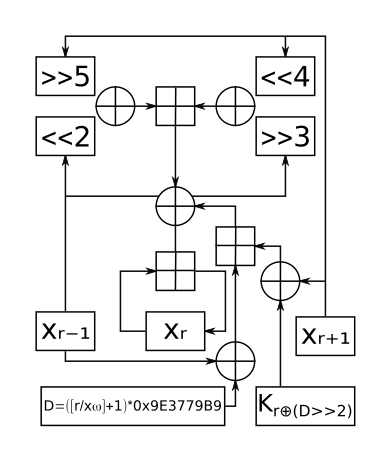
You can see from the graphics that there are add-ons, bits, bits, bits。
Process 1:
1. First teaEncryptionIt's in eight bytes, so it's four bytes from both sides
Two, four bytes to the right, which are referred to here as m, m, three parts, m, four to the left and the key, m, five to the right and the key, m, and last three to the same or the same
Three, four bytes to the left. Here's the four bytes called n, n = n + m
Process 2:
And then it goes down to this part where m and n swapped their positions
Two, four bytes to the right, three parts to the n, four to the left plus the key, five to the right plus the key plus the n to the right, three to the end, different values or
3 and 4 bytes to the left, m=m+n
Four, the m and n that you got at this point are the m and n that are encrypted
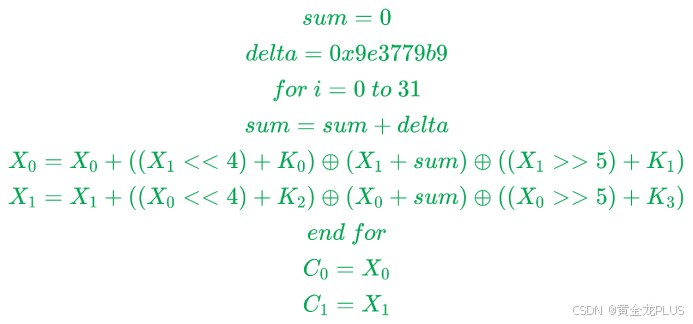
Decrypt
The decryption is..
+ = changed to - = left to right
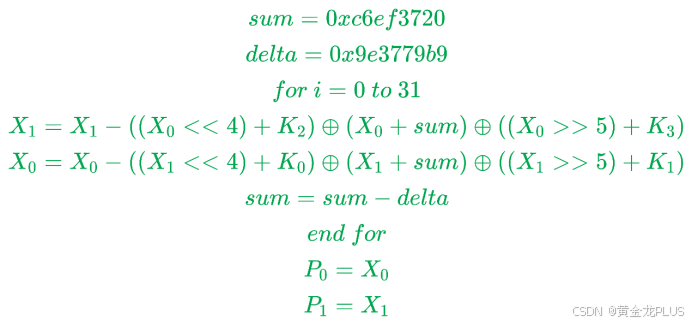
Script
One
Two
Three
Four
5
Six
Seven
8
9
10
Eleven
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
# i don't know #Oh, include
# i don't know #Oh, include

// encryption functions
I don't know @encrypt I'm sorryUint32 t♪ v,Uint32 t*k)Other organiser
    Uint32 tV0=v[v]0, v1=v[OneI'm sorry0I;
    Uint32 tDelta=0x9e3779b9;
    Uint32 tK0=k[k]0, k1=k[One, k2=k[Two, k3=k[Three];
    You know, for..(i)0;i 32;i++ {
Sum += delta;
V0 +=((v14)) + k0)^ (v1 + sum)^ ((v1>)5) + k1;
V1 + = ((v04)+k2) ^ (v0 + sum) ^ (v0 > >5) + k3;
♪ i'm sorry ♪
V[s]0=v0; v[v]One=v1;
♪ i'm sorry ♪

// decrypt function
I don't know Decrypt I'm sorryUint32 t♪ v,Uint32 t*k)Other organiser
    Uint32 tV0=v[v]0, v1=v[OneI'm sorry0xc6ef3720I;
    Uint32 tDelta=0x9e3779b9;
    Uint32 tK0=k[k]0, k1=k[One, k2=k[Two, k3=k[Three];
    You know, for..(i)0;i32;i++ {
V1 - = ((v04)+k2) ^ (v0 + sum) ^ (v0 > >5) + k3;
V0 - = ((v14)) + k0)^ (v1 + sum)^ ((v1>)5) + k1;
Som-= delta;
♪ i'm sorry ♪
V[s]0=v0; v[v]One=v1;
♪ i'm sorry ♪

Int I don't know( )
Other organiser
    Uint32 tV[s]Two== sync, corrected by elderman ==OneI don't know,Two♪ k[ ♪Four== sync, corrected by elderman ==TwoI don't know,TwoI don't know,ThreeI don't know,Four};
    / v for encryption is two 32-bit unsigned integers
    //k is encrypted decryption key, 4 32-bit integer, i. E. 128-bit key length
    I'm sorryI'm sorryOriginal data before encryption: %u %u\n,v[0,v[One(a) the following:;
Encrypt (v, k);
    I'm sorryI'm sorryEncrypted data: %u %u\n,v[0,v[One(a) the following:;
Decrypt(v, k);
    I'm sorryI'm sorry"data declassified: %u %u\n",v[0,v[One(a) the following:;
    Now 0;
♪ i'm sorry ♪
Reverse
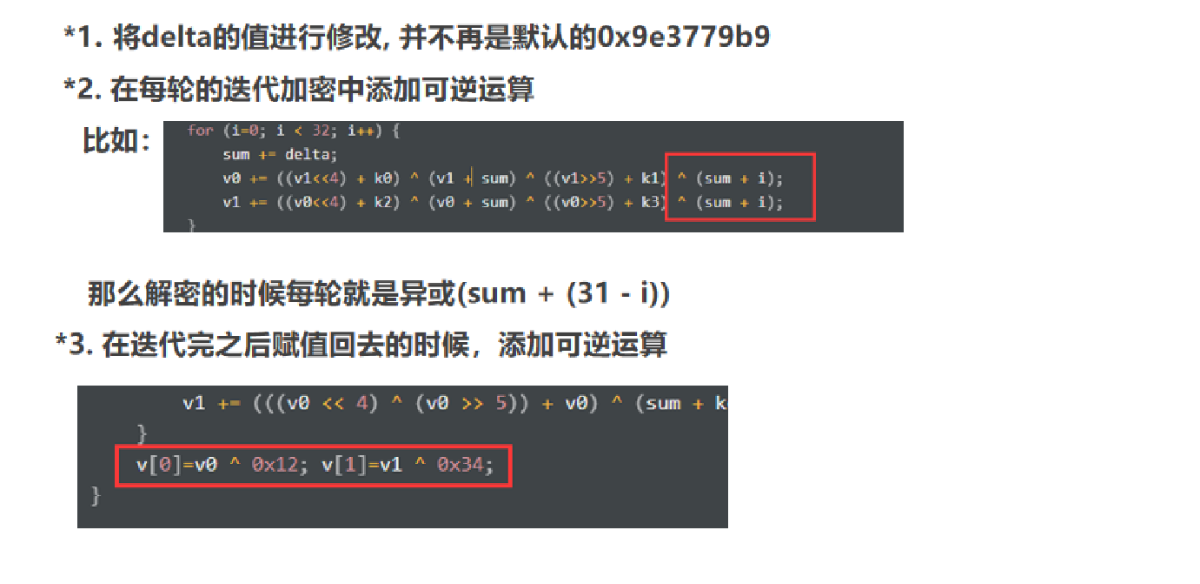
The 1-tea algorithm features the delta value and the 16 byte key (i. E. 128 bits)。
2. In reverse proceedings, the tea algorithm can be identified using the ida plugin findcypto
3, x-=0x61c88647 and x+=0x9e3779b9, both of which are equal
For example, this encryption function is v10-= 0x61c88647
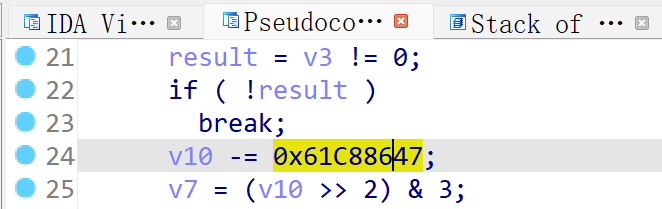
It's possible to start a compilation at +0x9e3779b9, but it's still -0x61c88647
Magic
Change the value of the ring
Xtea(extened tea)
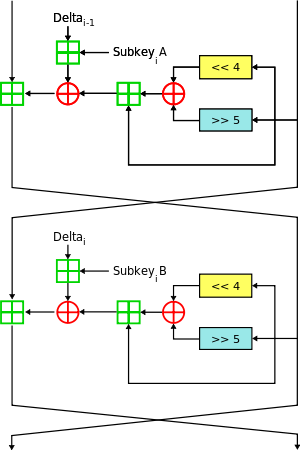
The tea upgrade, which fixes the key scheduling deficiencies of tea, adds more key lists, shifts, variations, etc.
Designer: roger needham, david wheeler
The tea algorithm was found to be flawed, and in response the designer proposed an upgraded version of tea - xtea (sometimes also known as “tean”). Xtea uses the same simple algorithm as tea, but it uses a very different sequence, and in order to prevent a key table attack, four subkeys (the original 128-bit key was split into 4 32-bit subkeys during the encryption process) are mixed in a less formal way, but at a slower rate。
Parameters and tea
Encryption
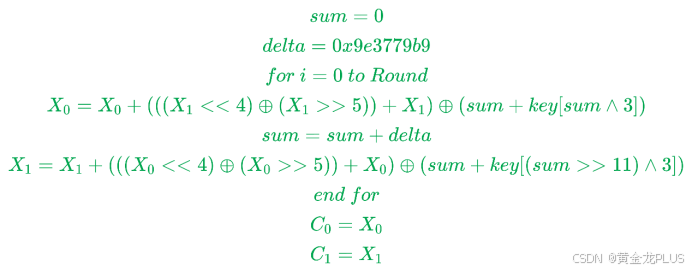
Decrypt
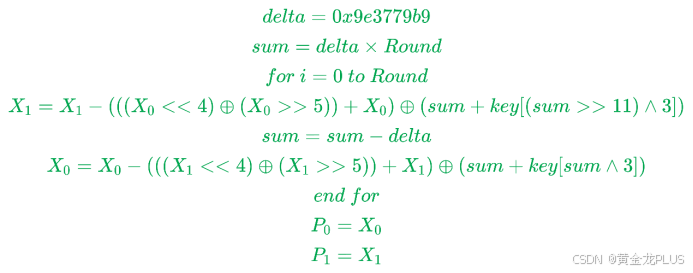
Script
One
Two
Three
Four
5
Six
Seven
8
9
10
Eleven
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
# i don't know #Oh, include
# i don't know #Oh, include


I don't know I'm sorryI'm sorryI'm sorry IntI'm sorry,Uint32 tV[s]TwoI don't know,Uint32 t ConstI don't knowFourI don't knowOther organiser
    I'm sorry IntI;
    Uint32 tV0=v[v]0, v1=v[OneI'm sorry0, delta =0x9e3779b9;
    You know, for..(i)0;i
V0 + = (((v1 4)(v1 > )5(sum + key[sum &Three(a) the following:;
Sum += delta;
V1 + = (((v0 4)(v0 > )5) + v0 (sum + key[(sum>]Eleven) &Three(a) the following:;
♪ i'm sorry ♪
V[s]0=v0; v[v]One=v1;
♪ i'm sorry ♪

I don't know I don't knowI'm sorryI'm sorry IntI'm sorry,Uint32 tV[s]TwoI don't know,Uint32 t ConstI don't knowFourI don't knowOther organiser
    I'm sorry IntI;
    Uint32 tV0=v[v]0, v1=v[One, delta=0x9e3779b9, sum=delta*num rounds;
    You know, for..(i)0;i
V1 - = (((v0 4)(v0 > )5) + v0 (sum + key[(sum>]Eleven) &Three(a) the following:;
Som-= delta;
V0 - =(((v1 4)(v1 > )5(sum + key[sum &Three(a) the following:;
♪ i'm sorry ♪
V[s]0=v0; v[v]One=v1;
♪ i'm sorry ♪

Int I don't know( )
Other organiser
    Uint32 tV[s]Two== sync, corrected by elderman ==OneI don't know,Two};
    Uint32 t ConstK[s]Four== sync, corrected by elderman ==TwoI don't know,TwoI don't know,ThreeI don't know,Four};
    I'm sorry IntR=32;/ /num rouds recommends 32
    / v for encryption is two 32-bit unsigned integers
    //k is encrypted decryption key, 4 32-bit integer, i. E. 128-bit key length
    I'm sorryI'm sorryOriginal data before encryption: %u %u\n,v[0,v[One(a) the following:;
Encipher (r, v, k);
    I'm sorryI'm sorryEncrypted data: %u %u\n,v[0,v[One(a) the following:;
Decipher(r, v, k);
    I'm sorryI'm sorry"data declassified: %u %u\n",v[0,v[One(a) the following:;
    Now 0;
♪ i'm sorry ♪
Xxtea(corrected extended tea)
Xtea upgrade. Sometimes it's called corrected block tea
Designer: roger needham, david wheeler
Block tea: the block tea algorithm can decrypt 32 integer variable blocks of any integer length by applying the xtea cycle function to every word in the block at a time and attaching it to the next word of the applied word。
Xteea uses structures similar to block tea, but uses adjacent words for each word in the processing block and replaces the xtea cycle function with an mx function with two input volumes. The adjacent words referred to above are actually the adjacent items of the array。
Further expand the "64-bit block" to a "longer field" and correct the differential attack vulnerability。
The length of the original string is not four times
Any explicit (each group) 4 bytes (32bit) may not be multiples, followed by 0
Secret
Same thing
32bit multiple
Key
16 bytes (128 bit)
Rounds
32 (recommended) ~ 64
Default 6+52 / n
Encryption
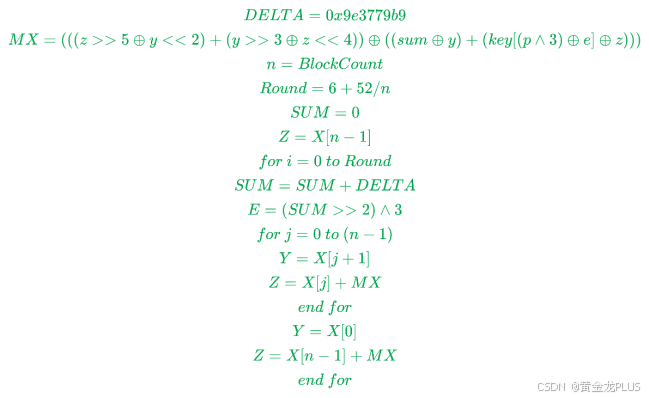
Number of encrypted wheels: rounds = 6 + 52 / n
Here i wonder why rounds = 6 + 52 / n, so i also collected the design principles for the number of encrypted wheels:
One
Total number of operations = rounds * n = (6 + 52 n) * n = 6n + 52
It can be seen as a fixed “cost” and regardless of the size of the data block, the total workload of encryption is more or less linear。
Of course, 52 of this formula is an empirical value that can strike a good balance between safety and performance at 52 hours。
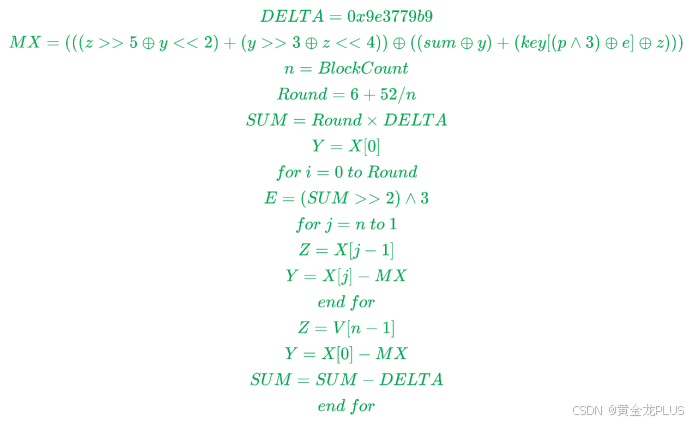
Decrypt
Script
One
Two
Three
Four
5
Six
Seven
8
9
10
Eleven
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
60
61
62
63
64
65
66
67
68
69
70
71
72
73
74
75
76
77
78
79
80
81
# i don't know #Oh, include
# i don't know #Oh, include
# i don't know #Oh, include
# i don't know #Oh, defineDelta 0x9e3779b9

Static Inline Uint32 t Mx calcI'm sorryUint32 tZ,Uint32 tYes,Uint32 tSom,Const Uint32 tI don't knowFourI don't know,I'm sorryP,I'm sorry(e)Other organiser
    Now((z > > )5(y 2)) + ((y > )Three(z 4)
^(sum ^ y) +(key [(p & )Three^e]^;
♪ i'm sorry ♪

I don't know Xxtea encryptI'm sorryConst Uint32 t# in, in #,IntNo, no, no,IntI don't know,Const Uint32 tI don't knowFourI don't know,Uint32 t♪ out ♪
Other organiser
    Uint32 tYes, z, sum0;
    I'm sorryIdx, cycle;

    Oh, memcpy(out, in,I'm sorryI'm sorryUint32 t* n);
= out [n--One];

    When(rounds --)
Sum + = delta;
Cycle = (sum > >)Two) &Three;

        You know, for..(idx =0;idx1;idx++ {
Y = out [idx +]One];
+ = mx calc(z, y, sum, key, idx, cycle);
Z = out [idx];
♪ i'm sorry ♪
Y = out0];
I don't know, outOne+ = mx calc(z, y, sum, key, n-One, cycle);
= out [n--One];
♪ i'm sorry ♪
♪ i'm sorry ♪

I don't know Xtea decryptI'm sorryConst Uint32 t# in, in #,IntNo, no, no,IntI don't know,Const Uint32 tI don't knowFourI don't know,Uint32 t♪ out ♪
Other organiser
    Uint32 tYes, z, sum;
    I'm sorryIdx, cycle;

Som = rounds * delta;
    Oh, memcpy(out, in,I'm sorryI'm sorryUint32 t* n);
Y = out0];

    When(rounds --)
Cycle = (sum > >)Two) &Three;

        You know, for..I'm sorryIntIdx = n--One;idx >0; idx-) {
= out [idx--One];
- = mx calc(z, y, sum, key, idx, cycle);
Y = out [idx];
♪ i'm sorry ♪
= out [n--One];
I don't know0-mx calc(z, y, sum, key,0, cycle);
Y = out0];
Sum - = delta;
♪ i'm sorry ♪
♪ i'm sorry ♪

I don't know PrintI'm sorryUint32 t♪ data ♪,IntI don't knowOther organiser
    You know, for..I'm sorryInt=0;i
        I'm sorryI'm sorry"%u ",data[i];
♪ i'm sorry ♪
    I'm sorryI'm sorry"what's wrong?";
♪ i'm sorry ♪

Int I don't know( )
Other organiser
    Uint32 tI don't knowTwo=One};/ policy for encryption data
    Uint32 tCiphertext[s]Two];
    Uint32 t ConstI don't knowFour=TwoI don't know,TwoI don't know,ThreeI don't know,Four};/key is the encryption decryption key for 4 32-bit integers, i. E. 128-bit key length
    Int=One;

    I'm sorryI'm sorry"the original data before encryption:;
Print(plant, n);
Xxtea encrypt,Six+52/n, key, vipertext;
    I'm sorryI'm sorry"data encrypted:;
Right, n;
Xxtea decrypt,Six+52/n, key, policy);
    I'm sorryI'm sorry"data declassified:;
Print(plant, n);
    Now 0;
♪ i'm sorry ♪
Maybe we can look at that 1z re









